

Password Policies
Password policies define the rules that every password used to access the platform must follow: length, complexity, expiration, and lockout after failed attempts. On the same screen, you can also automatically lock users who have gone too many days without accessing the platform. This way, forgotten accounts, such as those belonging to people who have left the company, do not remain open.
Before you begin
Access is usually restricted to administrators. The password rules apply to all users who sign in with a Dattos username and password. The access inactivity lockout has its own rules, explained below.
Accessing password policies
Click the gear icon in the upper-right corner, then in the Admin Menu select Security → Password Policies.
Adjust the rules (described below) and click Save.
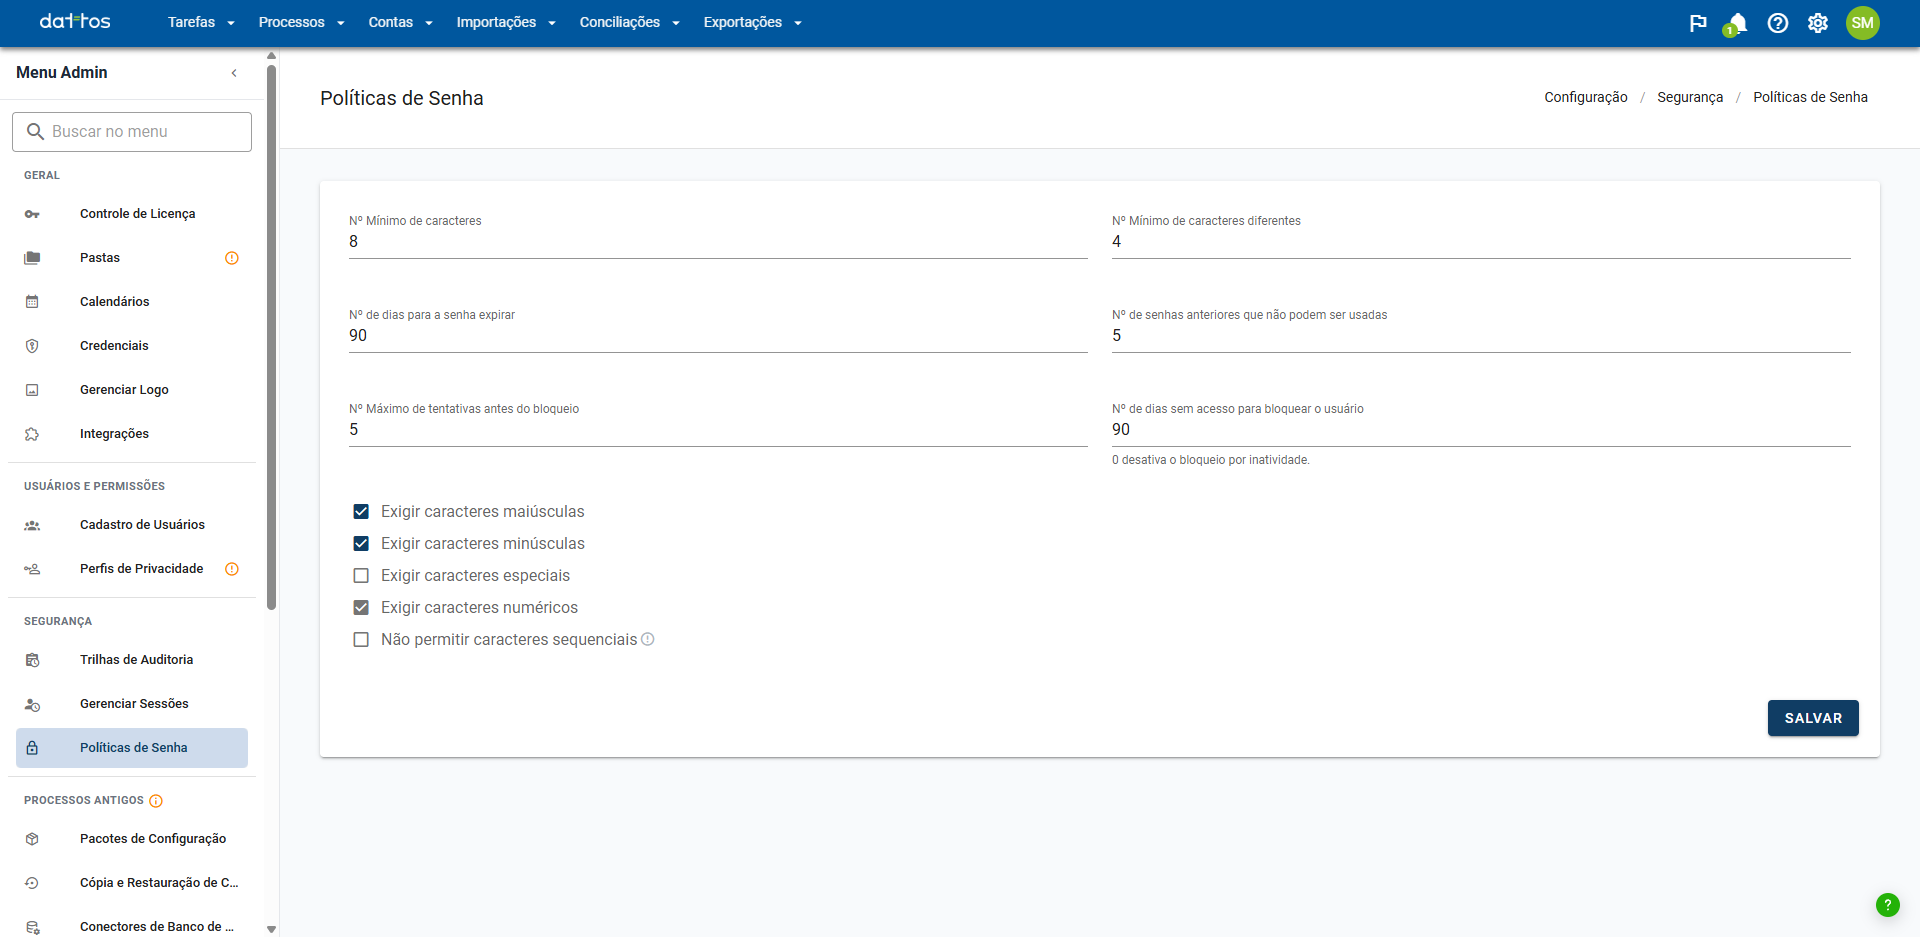
Available rules
Each rule has a recommended starting value:
Minimum number of characters: minimum password length. Recommended:
8.Minimum number of different characters: how many characters must be distinct. For example, with a minimum of
1, the passwordAAAis invalid andAABis valid. Recommended:1.Number of days before the password expires: password validity period, counted from the last change. Recommended:
90.Number of previous passwords that cannot be used: prevents the reuse of the most recent passwords. Recommended:
3.Maximum number of attempts before lockout: incorrect login attempts before the system blocks access. Recommended:
3.
There are also composition requirements, which we recommend leaving selected:
Require uppercase characters (e.g.,
ABCDE).Require lowercase characters (e.g.,
abcde).Require special characters (e.g.,
!@#$%).Require numeric characters (e.g.,
12345).Do not allow sequential characters: prevents three or more characters in sequence, such as
abc,987, orqwe.
Important: the recommended values are only a best-practice guideline. Always follow the password guidelines defined by your company.
Lock users without access
The Number of days without access before locking the user field automatically locks anyone who has gone more than this number of days without accessing the platform. For example, with 90, anyone who has not signed in for more than 90 days is locked.
Disabled by default. The value
0disables inactivity lockout (the screen itself reminds you of this just below the field), and this is the value initially set in the field. Nothing is locked until someone enters a number of days and saves. Negative values are not accepted.Applies to users who sign in through the company login. Automatic lockout only affects users when the environment uses the company's single sign-on (SSO). If the environment uses a Dattos username and password, it does not lock anyone on your team; in that case, access is controlled by password expiration and login attempts.
Runs once a day. The platform checks access daily and locks anyone who has exceeded the limit. Users who are already locked remain as they are.
Counts from the last login. What matters is the last time the person accessed the platform. A newly registered user has the registration date as the starting point, so they are not locked before having a chance to sign in.
Is recorded. Each automatic lockout appears in the Audit Trails with its own origin, separate from lockouts performed manually. Changes to the number of days are also recorded, like changes to the other rules.
To unlock someone, go to Admin Menu → Users and Permissions → User Registration, open the person's record, clear the Locked option, and save. Ask them to access the platform immediately afterward: until there is a new login, the last access remains old, and the following day's check may lock them again.
Tip: a user locked due to too many attempts, lack of access, or manual action must contact the platform administrator on their team. The lockout also applies to users who sign in through the company login (SSO): they can only sign in again after being unlocked on the User Registration screen.