Privacy profiles
Privacy profiles are how you precisely control what each person can access in Dattos. Instead of configuring permissions user by user, you create a profile (a group of users who share the same rights) and manage everything from there.
A profile brings together, in one place, which screens the group can see, which analyses it can run, what it can edit, and which approval levels it is responsible for.
Before you begin
Creating a profile always follows three steps, in this order: you create the profile, define its permissions in the configuration tabs, and assign the users who will inherit them. The sections below follow this sequence.
Creating a privacy profile
Click the gear icon in the upper-right corner, then under the Admin Menu, choose Users and Permissions → Privacy Profiles.
Click New.
In the Profile Data tab, enter the name and description, then click Save to enable the remaining tabs.
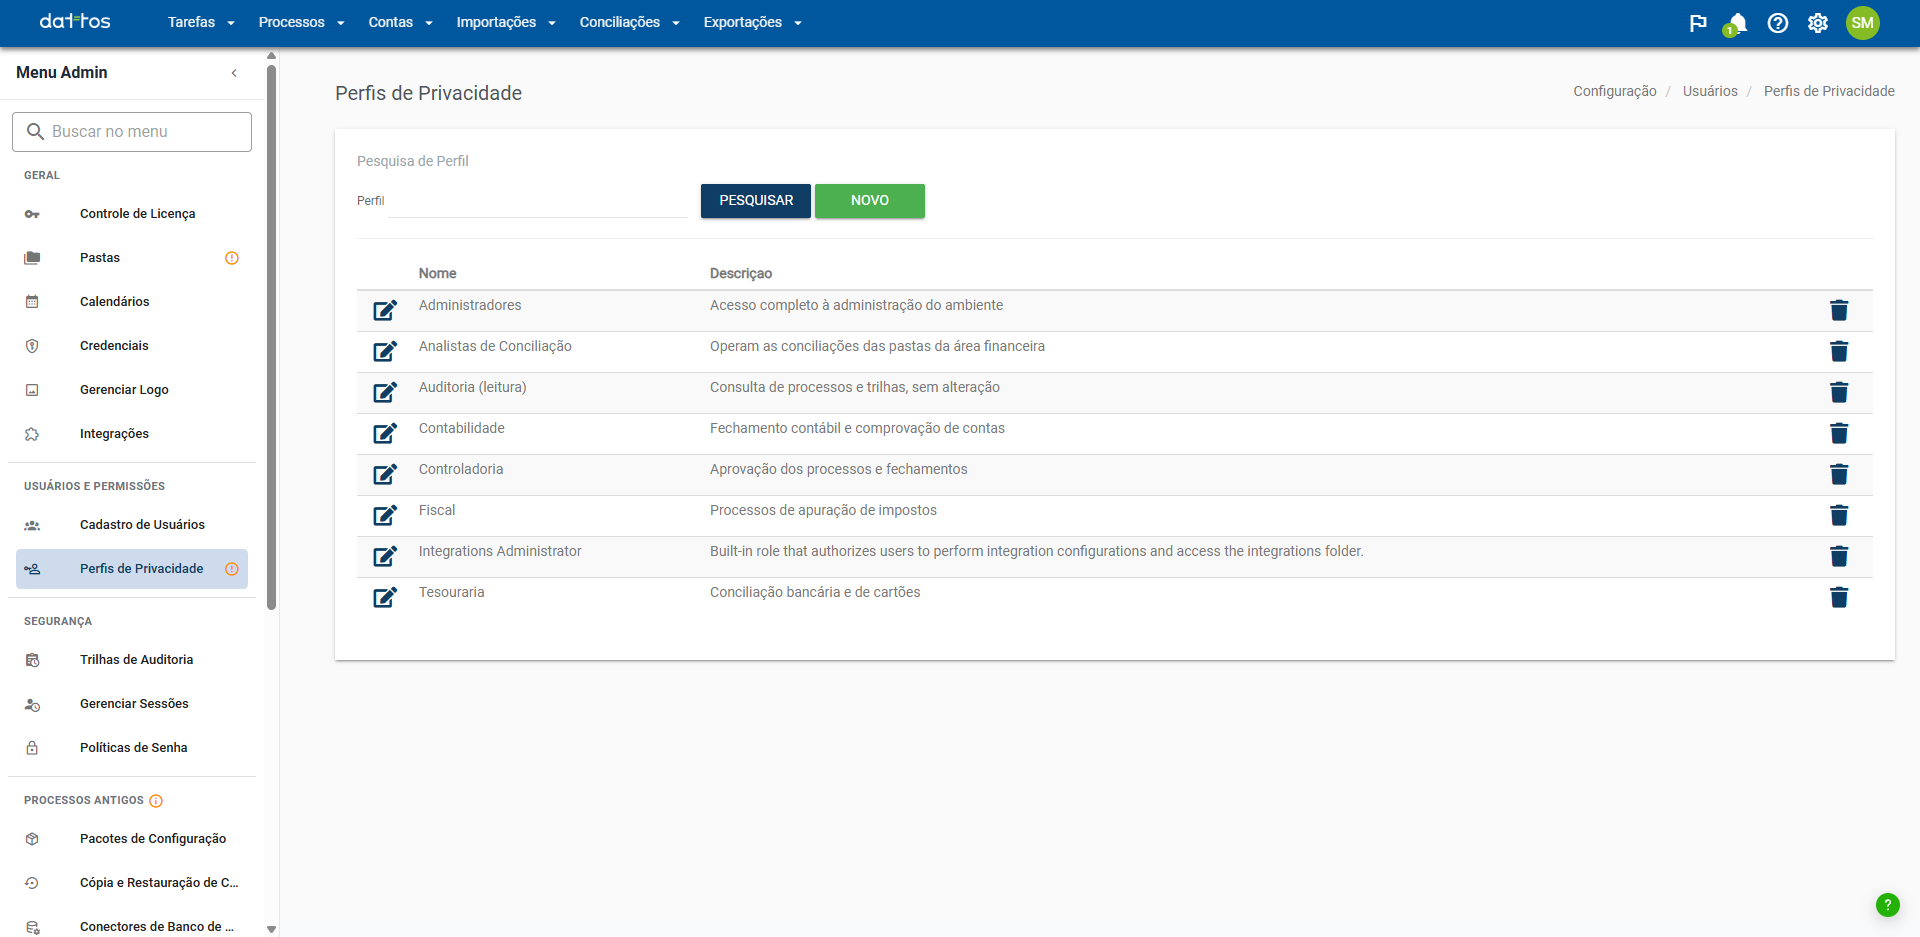
The screen opens to the list of profiles already registered. Use the Profile field and the Search button to find a profile by name, the pencil icon to edit it, and the trash can icon to delete it.
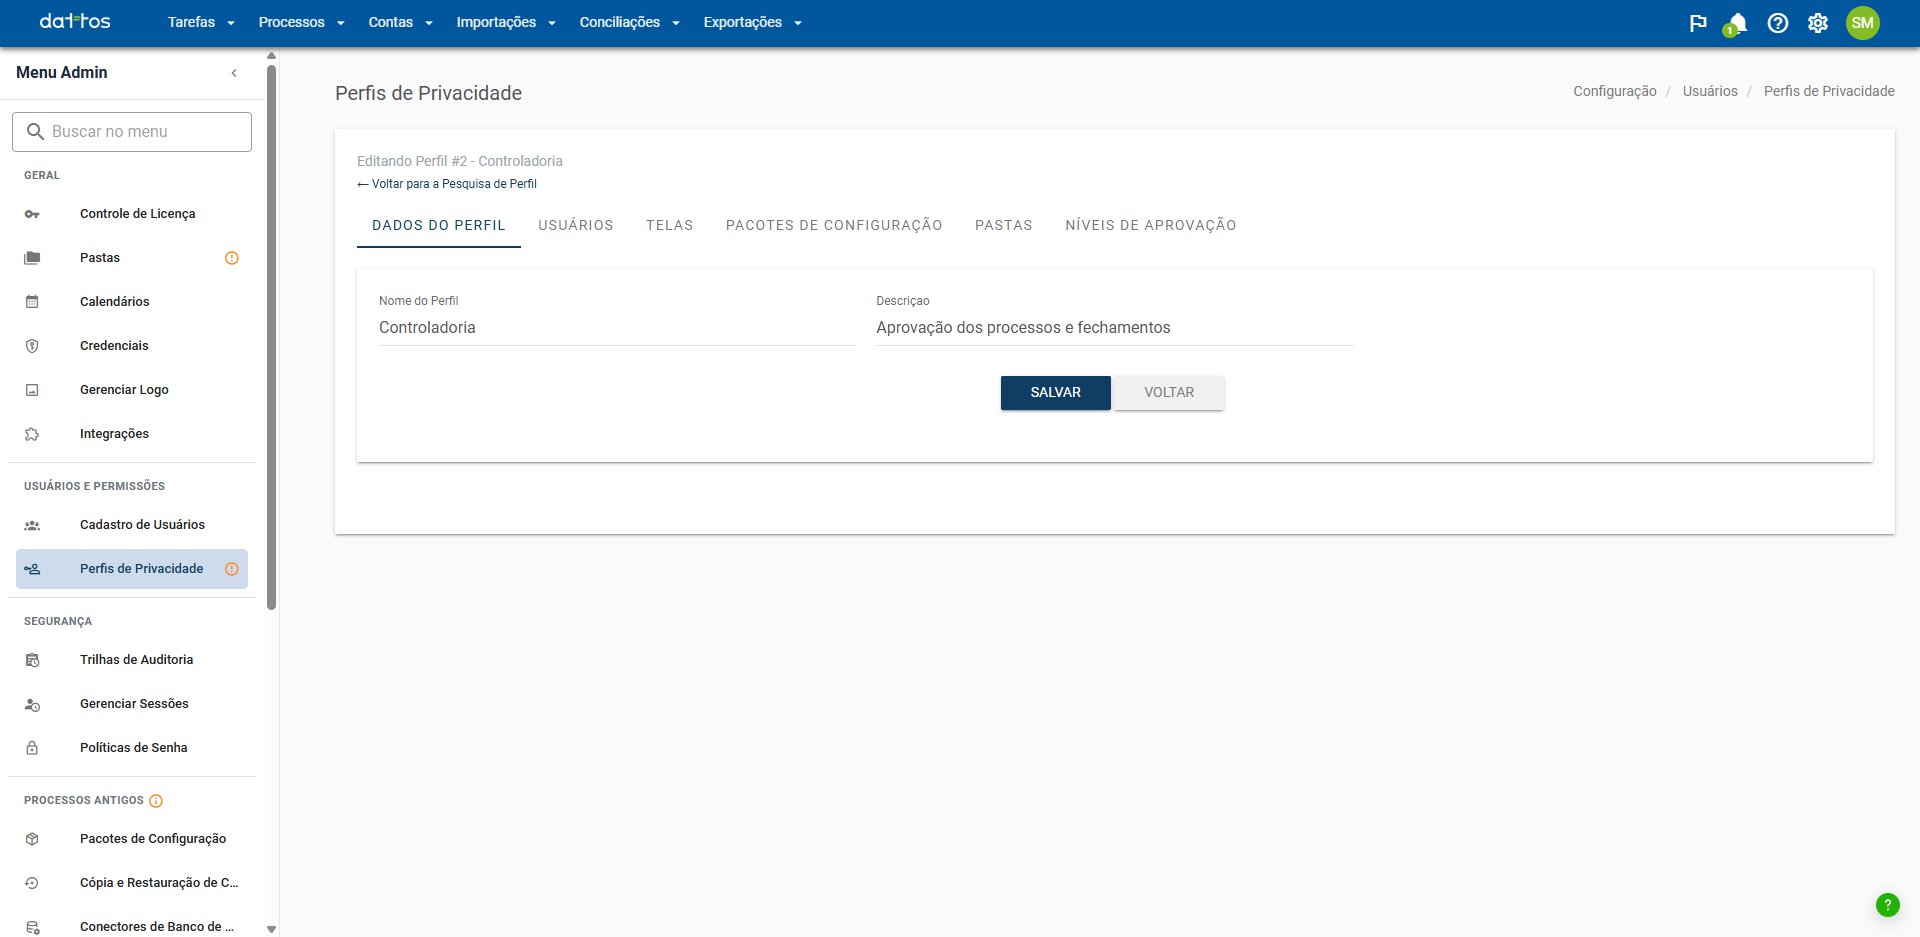
In the Profile Data tab, enter:
Profile Name: the name displayed in permission assignments, with up to 50 characters and no duplicate profile names. Example:
Preparadores.Description: a short text explaining the profile's responsibility, with up to 100 characters. Example:
Preparadores de análises financeiras.
Configuring profile permissions
After you save, the configuration tabs become available. Each one controls a dimension of the group's access: who participates, which screens they can navigate, what they can configure, which folders they can see, and which approvals they can perform.
Important: the Save button saves only the tab currently open. Save each tab before moving to the next one, or the selections made in it will be lost.
Users
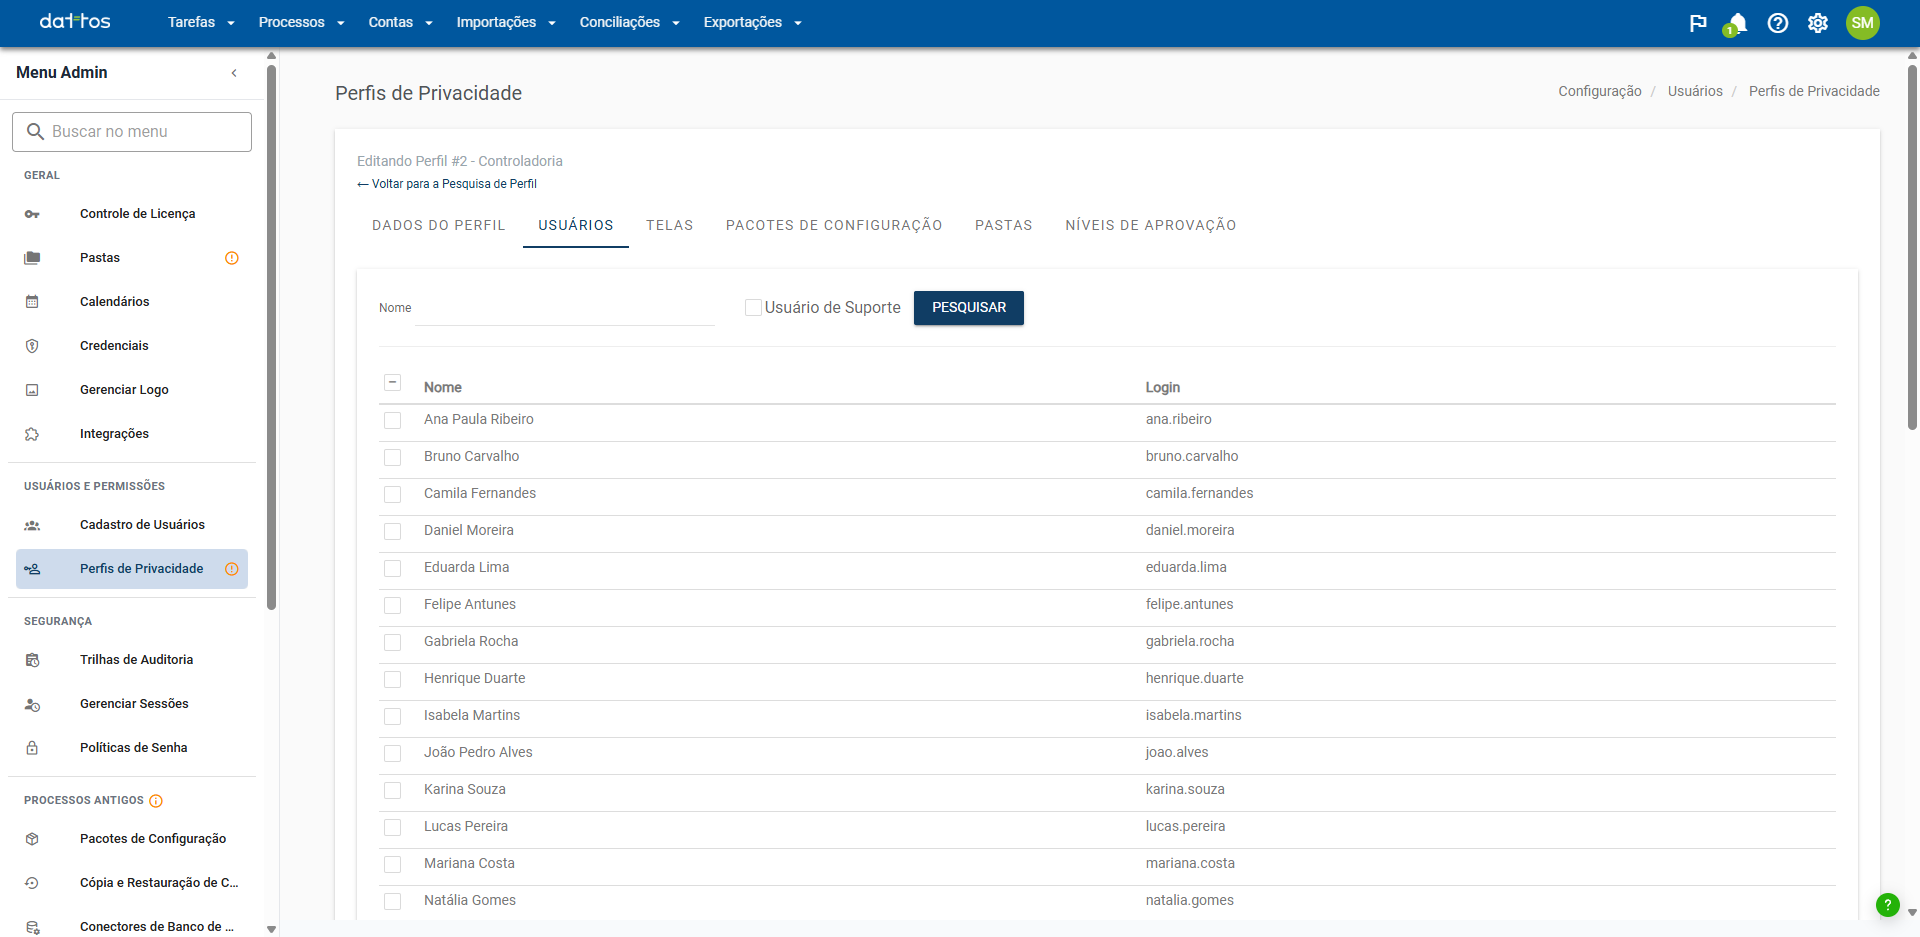
In the Users tab, select the people who belong to the profile. Use the Name field and the Search button to find someone. They will all share the permissions configured in the other tabs. A user can belong to more than one profile, and the association can also be made in the user's record, in the Profile tab.
Important: permissions are cumulative. When a user belongs to more than one profile, they accumulate the permissions from all of them. On screens with conflicting levels, the higher permission prevails (Write takes priority over Read).
Screens
The Screens tab defines which platform pages the group can navigate. Use Page Name to find a screen. Each screen accepts one of three permission levels:
Write: the user can view the page and perform actions on it (import data, provide justifications, delete, comment, and so on).
Read: the user can view the page but cannot interact with action buttons.
None: the user cannot view the page.
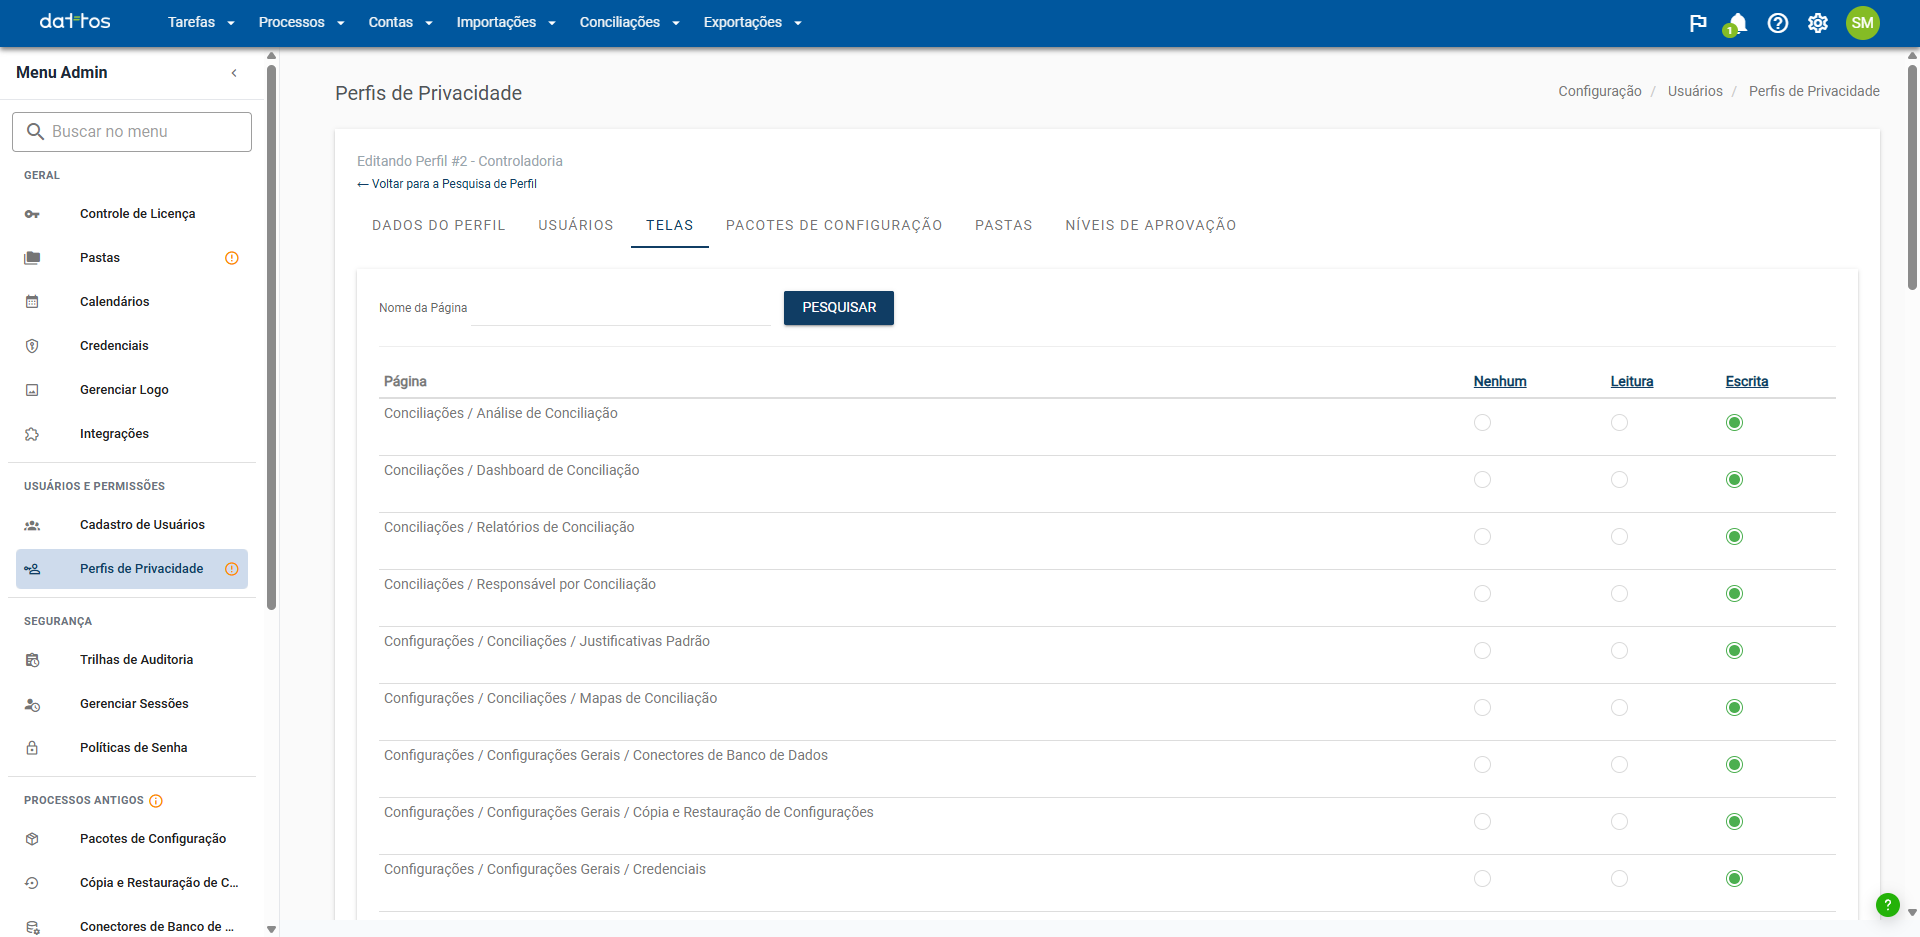
Process access
Since version 16.5, process access is also defined in the Screens tab, rather than within each process. There are three areas, each with the same three levels:
Analysis: view and operate the process result. With Write, the group can run the process.
Process Settings: the configuration tabs. With Write, the group can change the configuration.
Process Construction: the data flow editor. With Write, the group can change the flow.
To open a process, you must have at least Read in one of these areas. Details are available in the Permissions article.
Configuration Packages
Configuration packages are reusable containers that separate an analysis's logic from its execution information. In the Configuration Packages tab, select the packages that the group will be able to view on configuration screens. Use Configuration Package Code or Name to find a package.
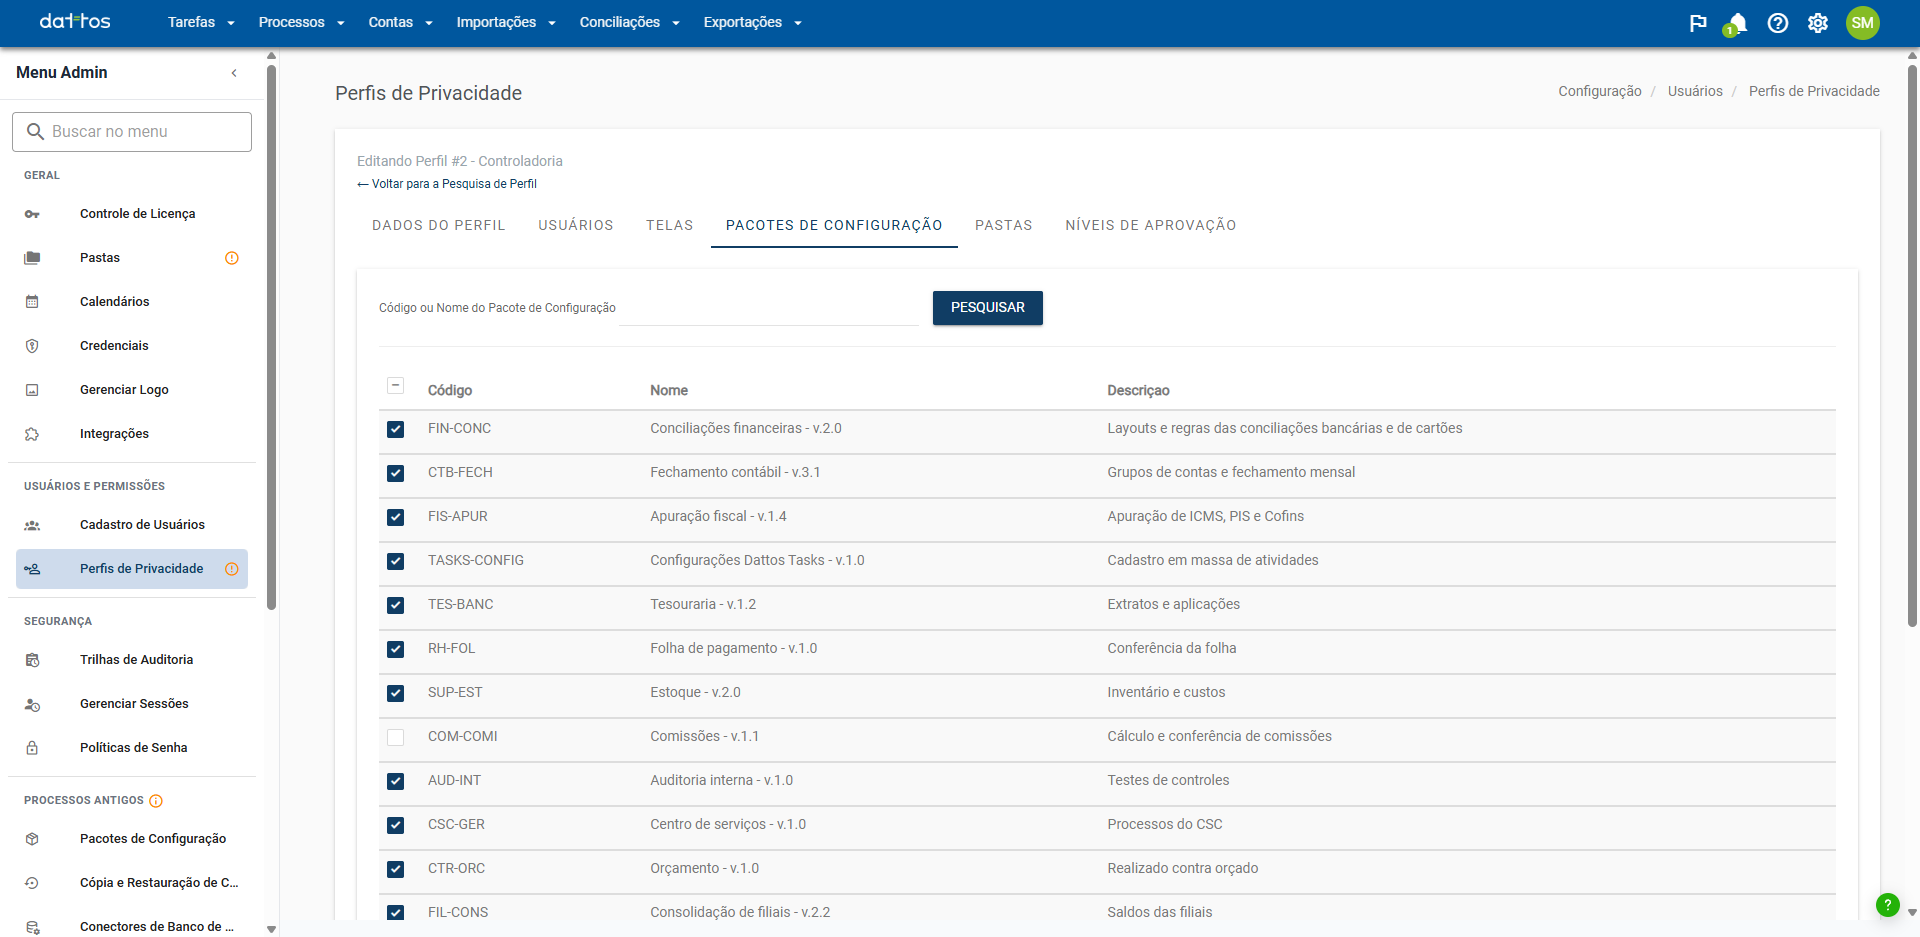
Important: viewing is not editing. To change a configuration, the user needs Write permission on the related screen and access to the corresponding package. Example: to adjust the reading of an Excel file, they need Write permission on the Import Layouts screen and access to the desired package.
Configuration packages belong to the legacy configuration screens. In environments where these screens have been disabled, the tab is unavailable.
Folders
Folders organize the platform's analyses, so this is where you define what the group can see. In the Folders tab, select the folders that the group will be able to view on analysis screens. Use Folder Code or Name to find a folder in the tree. Remember that granting access to a folder does not authorize editing the configurations of the analyses it contains.
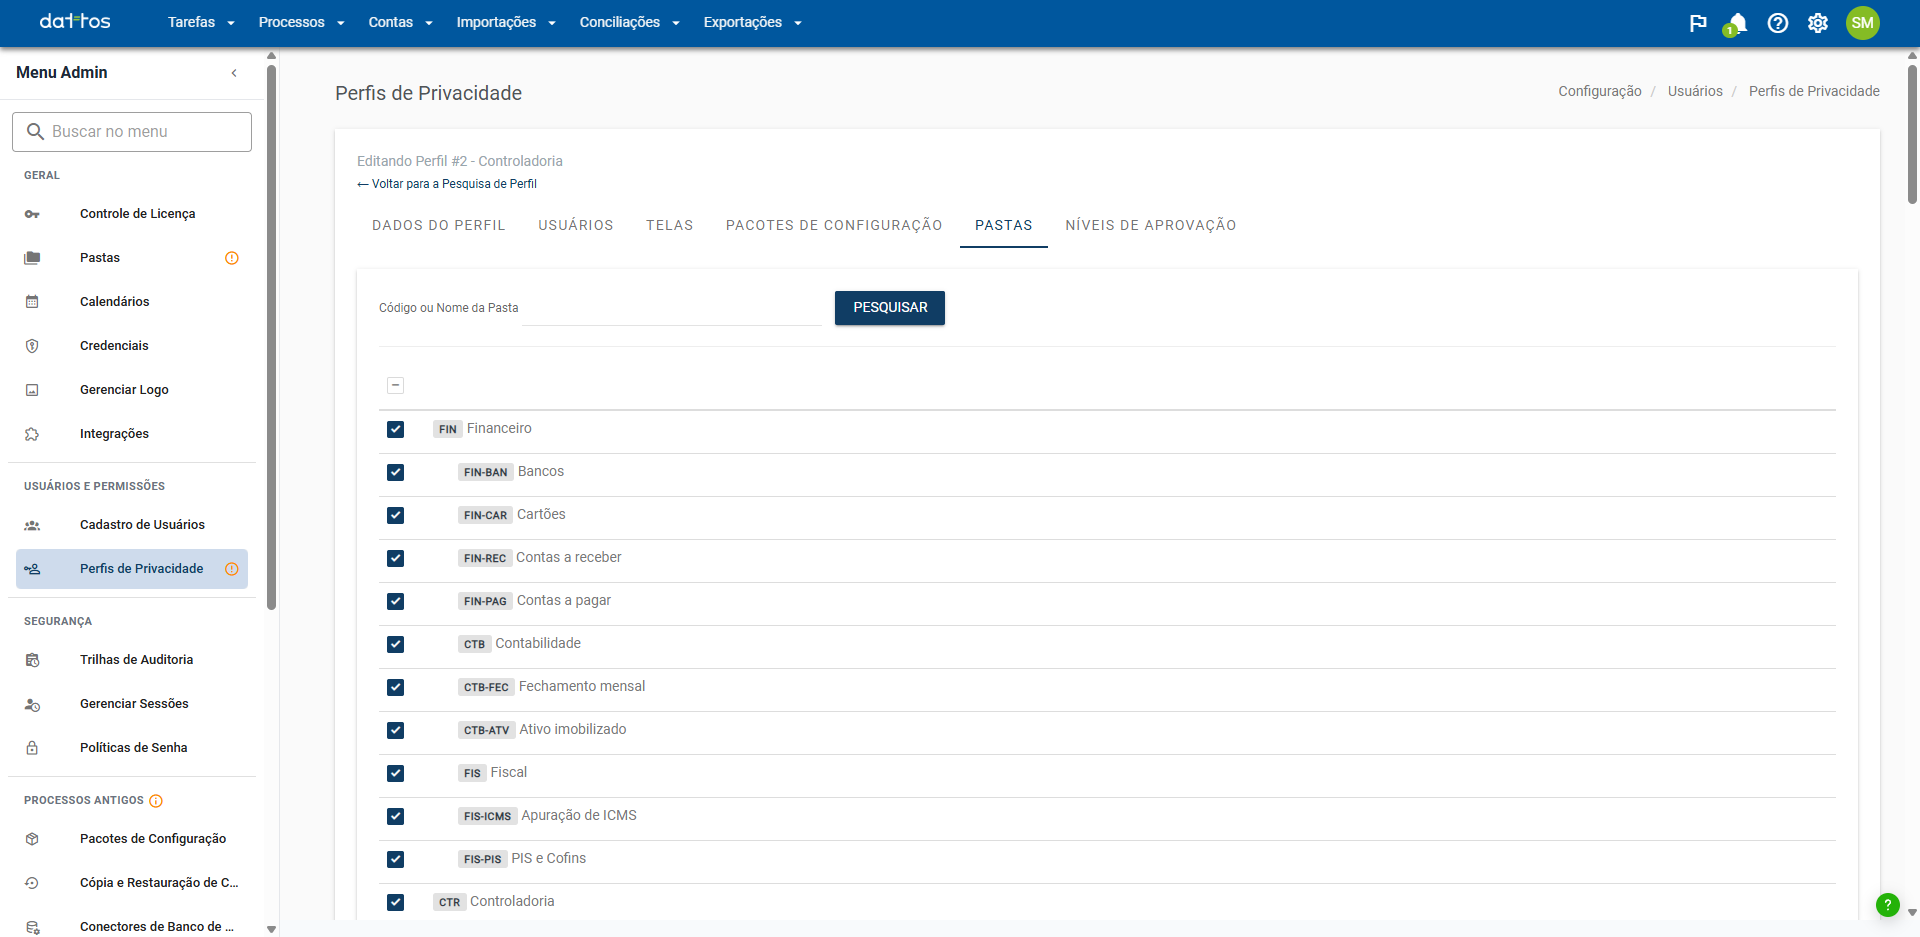
Two things to keep in mind about folders:
Anyone with access to a folder has access to all its processes, at the level defined in the Screens tab. To separate access, place the processes in different folders.
When you select a folder, the screen also selects the folders above it and the folders inside it. You can then deselect only some subfolders.
Once saved, each folder stands on its own. A subfolder created later is not made available simply because it is inside an available folder: it must be selected in the profile.
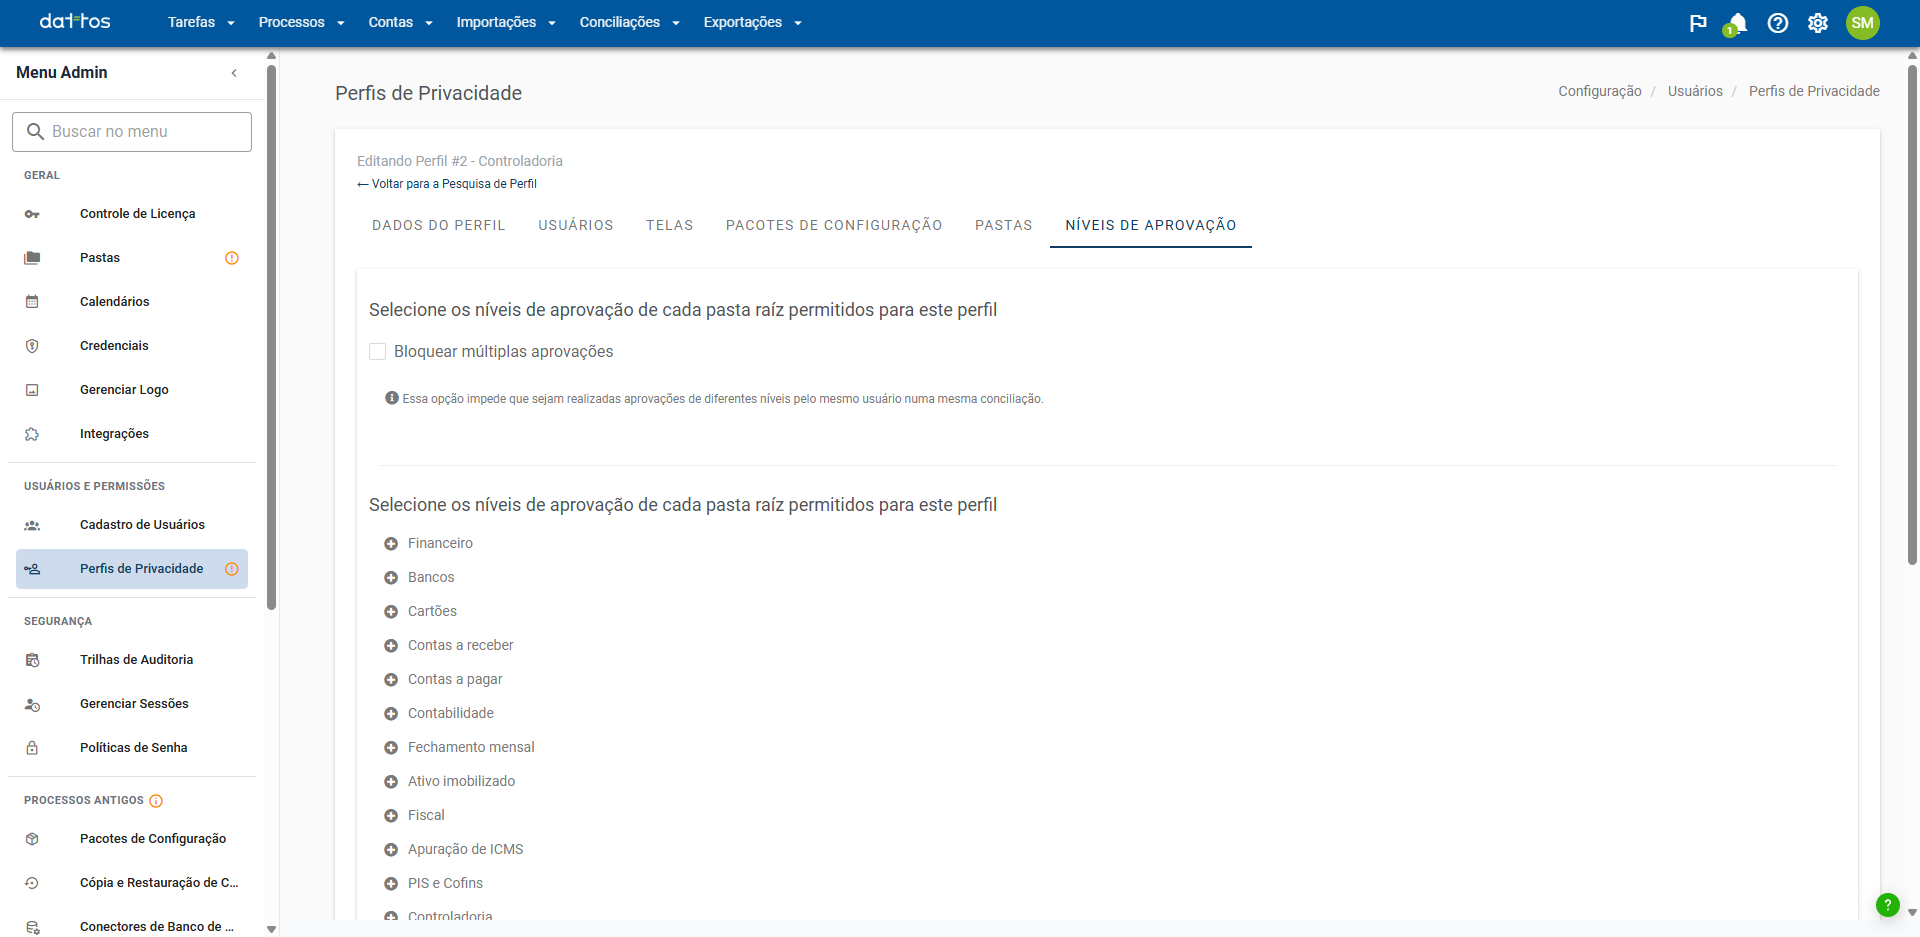
Approval Levels
The Approval Levels tab defines what the group can approve: for each root folder, choose which levels of the approval flows the group can advance or revert. The names and order of these levels come from the root folder's record.
There is also an option to strengthen control:
Block multiple approvals: when selected, it prevents the same user from approving different levels of a flow within the same reconciliation.